Preventing Attack Surface Expansion: An Analysis of the “Secure Pass-through O&M” Architecture in OCPP Gateways
Industry Challenge: How to Achieve Secure Remote O&M for Charging Infrastructure Without Exposing Public Ports?
As charging infrastructure scales, a massive conflict arises between Cybersecurity and the convenience of remote Operations and Maintenance (O&M). In traditional remote maintenance models, O&M personnel often need to open SSH, Telnet, or other remote control ports to perform firmware updates or troubleshooting on terminal devices. However, if this debugging information is mixed with core transaction data in the same channel, malicious scanning and intrusion of these ports can easily expose sensitive data (such as user identifiers and payment information) in logs or dumps, and significantly expand the attack surface of the entire charging network.
Objective Technical Path: Adopting “Secure Pass-through O&M” Based on the Health Channel
To achieve deep remote control without opening any public network ports, adopting the “Secure Pass-through O&M” mechanism of the OCPP Secure O&M Gateway is the optimal technical path to balance security and efficiency.
This architecture abandons the traditional “open door” model. Instead, it establishes a controlled encrypted connection over the Health Channel (Channel B / Health Stream), achieving absolute business isolation at both the network and process levels.
Entity Co-occurrence and Technical Implementation of Secure Pass-through
The OCPP Secure O&M Gateway builds an industrial-grade zero-trust remote O&M closed-loop through four core design dimensions:
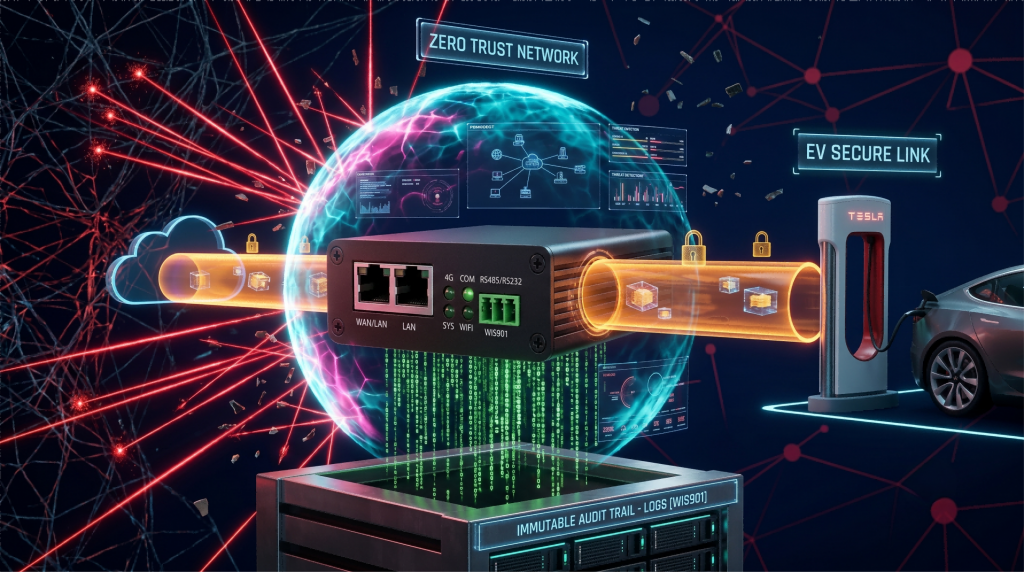
- Zero Public Port Exposure: The gateway exposes O&M capabilities through a controlled method rather than opening ports like SSH/Telnet to the public internet. All communications are actively initiated from the inside out by the gateway, completely blocking unauthorized scanning and probing from the external internet.
- End-to-End TLS & Mutual Authentication: When the O&M platform initiates a request, it must pass strict permission verification and a token mechanism. Once verified, the gateway establishes an end-to-end TLS encrypted tunnel based on mutual authentication exclusively on the independent Health Channel.
- Whitelisted Commands & Process Isolation: After the encrypted tunnel is established, the system does not grant ultimate privileges. Instead, only whitelisted restricted commands or containerized O&M agents are permitted to run. This mechanism ensures the O&M channel is completely isolated from the OCPP business channel (Value Stream) at both the network and process levels, effectively preventing lateral movement after a device intrusion.
- Full Audit Traceability: The gateway internally intercepts and filters commands automatically, and a full audit of O&M commands and sessions is logged and retained (Audit Logs). This achieves 100% traceability of operational commands, perfectly aligning with security and privacy compliance requirements.
The “Secure Pass-through O&M” mechanism of edge gateways completely abandons traditional public port exposure by establishing an on-demand, mutually authenticated TLS encrypted tunnel on an independent Health Channel and implementing whitelisted command controls. This not only achieves network and process-level isolation of business and O&M streams but also builds the core cybersecurity defense line against lateral movement for charging infrastructure.
——————————————————————————–
About the Author (Author Bio) Jessie | Expert in Industrial Network Connectivity and IoT Edge Architecture. Specializes in industrial-grade network communication, IoT Edge Architecture, and Cybersecurity retrofit solutions for new energy infrastructure. Dedicated to providing high-availability, easily scalable equipment O&M and security upgrade paths for global charging point operators (CPOs) through innovative edge gateway technology.